Category: News

Hashtag Trending Mar.5- Apple Music fined for market dominance; LockBit back from the dead; OpenAI kills ChatGPT plugins

Apple Music gives a whole new meaning to the phrase the hits just keep on coming.  It’s not the opposing candidates, it’s public AI systems that are spreading election disinformation, and LockBit, the cybercriminal gang may be back from the dead and saying so long to the ChatGPT plugins, which went from innovation to legacy in only a few months.


All this and more on the “they were so 2023” edition of Hashtag Trending. I’m your host, Jim Love, CIO of IT World Canada and TechNewsDay in the US.

The European Commission has imposed a fine of about a billion dollars US on Apple for what it claims is Apple’s abuse of its dominant market position in the distribution of music streaming apps through its App Store. 

The Commission found that Apple had implemented restrictions on app developers, preventing them from informing iOS users about alternative and more affordable music subscription services available outside the app, known as “anti-steering provisions.” Such actions are deemed illegal under EU antitrust rules.

This latest action from the European commission was initiated by a complaint from Swedish music streaming service Spotify.

Margrethe Vestage, the executive vice president in charge of competition policy, said, “For a decade, Apple abused its dominant position in the market for the distribution of music streaming apps through the App Store. They did so by restricting developers from informing consumers about alternative, cheaper music services available outside of the Apple ecosystem. This is illegal under EU antitrust rules, so today we have fined Apple over €1.8 billion.” 

Apple, being the sole provider of an App Store for iOS users across the European Economic Area (EEA), controls every aspect of the iOS user experience, including the terms and conditions developers must comply with to reach iOS users. 

The Commission’s investigation highlighted that Apple’s anti-steering provisions banned developers from:

Informing iOS users within their apps about subscription offers available on the internet outside of the app.
Informing iOS users within their apps about the price differences between in-app subscriptions sold through Apple’s in-app purchase mechanism and those available elsewhere.
Including links in their apps that lead iOS users to the app developer’s website where alternative subscriptions can be purchased. Additionally, app developers were restricted from contacting their newly acquired users, for instance, by email, to inform them about alternative pricing options after setting up an account.

Apple has taken a series of hits from the European Commission, on its app store and now on its music service. It faces class action lawsuits about its closed system that forces users to pay for iCloud backups, this last action happening in the U.S.. But clearly Apple’s closed system, the thing that has made them a multi-trillion dollar company, is under attack.

Apple has said it will appeal the order and maintains that consumers were not harmed by their actions and that Spotify had also not suffered any harm as they sell their subscriptions from the Spotify website and don’t have to pay Apple anything.

Source include: 

A recent study has revealed that public AI chatbots have been spreading false and misleading information about the 2024 election. 

This came from research conducted by the AI Democracy Projects and Proof News, underscoring the critical need for regulatory oversight as AI increasingly influences political discourse.

The study tested various AI models, including OpenAI’s ChatGPT-4, Meta’s Llama 2, Anthropic’s Claude, Google’s Gemini, and Mistral’s Mixtral, and found them all guilty of giving voters incorrect polling locations, illegal voting methods, and false registration deadlines. 

For example, Llama 2 incorrectly claimed that California voters could vote via text message, an illegal method in the United States. Additionally, none of the AI models tested could accurately identify the prohibition of campaign logo attire at Texas polling stations, such as MAGA hats.

This spread of misinformation has prompted responses from the AI developers. Anthropic plans to release an updated version of its AI tool with accurate election information. OpenAI has expressed intentions to refine its approach. However, Meta dismissed the findings as “meaningless” and that has sparked controversy and raised questions about their commitment to curbing misinformation.

That attitude from Meta could come at a cost as it may place pressure on the government to increase regulations on AI systems – although that may not be considered a bad thing by election officials – or the public.

Sources include: 

The Federal Bureau of Investigation (FBI) and the UK’s National Crime Agency, along with agencies from ten countries, collaborated in Operation Cronos to target the LockBit ransomware gang, one of the world’s most successful ransomware groups. This operation, which began on February 20, led to the takedown of over 30 servers, acquisition of source code, decryption keys, affiliate details, chat logs, and more, effectively disrupting LockBit’s operations.

The agencies involved in the operation added a twist of humour to their takedown by altering the traditional “Game over” message seen by users trying to connect to the seized sites. They included a loading animation featuring the flags of the agency consortium and embedded images with jokey file names. Additionally, they replicated LockBit’s countdown timer, which typically indicated the time left for victims to pay up, to count down to the unmasking of LockBit’s leader, known as LockBitSupp.

LockBit, which emerged in 2019, had become the most successful ransomware gang by adopting a business-oriented model. It provided tools and managed negotiations with victims in exchange for a 20 percent cut from its affiliates, who conducted the actual hacking. The gang’s professional online presence and marketing strategies were notable, even running bug bounty programs to improve its operations and security.

But it may turn out that Lockbit may have the last laugh on this one.

Despite the initial success of Operation Cronos, LockBit and LockBitSupp resurfaced online just five days later, with LockBitSupp mocking the federal agencies’ efforts.

 The FBI and its partners had anticipated this comeback, emphasizing that they had obtained keys to assist thousands of victims. The future rounds of this ongoing battle between law enforcement and the LockBit gang will determine the ultimate victor.

But it may have turned out that LockBit may have had a better recovery plan than most of its victims.

Sources include: 

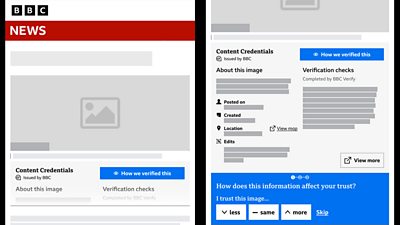
BBC News has launched a new “content credentials” feature, designed to prove the authenticity of images and videos used in their journalism. 

This feature, part of BBC Verify, allows users to see a button labeled “how we verified this” beneath images and videos on the BBC News site. Clicking on this button reveals the verification processes undertaken by BBC journalists, such as cross-referencing content with other sources, examining metadata, comparing locations, and checking for the correct casting of shadows, among other methods.

This initiative aims to counter the spread of disinformation, AI-generated deepfakes, and other forms of manipulated content. It also seeks to help audiences distinguish between real and fake BBC content when encountered on external sites. 

Deborah Turness, CEO of BBC News, emphasized the importance of earning trust by showing audiences not just what the BBC knows, but how it knows it, highlighting the significance of transparency in today’s environment of deep fakes and misinformation.

The “content credentials” feature incorporates a new technical standard that embeds information about the origins of media, including how it has been edited, functioning like an audit trail. This standard, developed by the Coalition for Content Provenance and Authenticity (C2PA) co-founded by BBC Research & Development, Adobe, and Microsoft, is freely available and has seen participation from major organizations like Google, Facebook, and OpenAI.

Initially, content credentials will be available on select content published by the BBC Verify team on the BBC News site and app. 

Future plans include working with external publishers and social media networks to ensure these credentials are displayed wherever news is consumed, aiding in the quick identification of genuine BBC content.

Sources include:  BBC 
And finally, OpenAI is doing away with its plugins. These functions, added by third party developers, extended the functionality of OpenAI. The first, and in my mind, still the best way of linking ChatGPT to the internet is via a plug-in.

What will replace the plug-ins? Apparently, ChatGPT wants to use its GPT’s – the feature that they introduced recently that allows anyone to write their own mini-GPT model that can also now be called from another chat session.

That has a couple of problems. One, the plug-ins were created and tested to perform their functions and while there are a lot of them, they also had some kind of quality control.

GPTs, on the other hand, might be a great idea, but were launched with no quality control and the number of them – one estimate was more than three million – makes it difficult to even conceive of how to sort through the mess and replace some of the plugins that users have come to count on.

A lesson to all of us – these public AI models are evolving rapidly and they may not feel an obligation to support any legacy functions. And in the world of AI, a “legacy function” could be measured in months, giving little time to react.  


That’s our show for today.

Love your comments. 

Send us a note at jlove@itwc.ca or drop us a comment under the show notes at itworldcanada.com/podcasts – look for Hashtag Trending. 

Thanks for listening and have a Terrific Tuesday.


The post Hashtag Trending Mar.5- Apple Music fined for market dominance; LockBit back from the dead; OpenAI kills ChatGPT plugins first appeared on IT World Canada.

Is the BlackCat/AlphV ransomware gang self-destructing?

The ongoing saga of the BlackCat/AlphV ransomware gang continues, with a news report that the crew has shut down its servers after a controversial hack of an American healthcare services provider.

Bleeping Computer says the gang’s data leak blog shut on Friday and the sites it uses to negotiate ransom payments closed today.

This comes after

— a gang affiliate last month was allegedly paid US$22 million after its data theft and ransomware attack disrupted the services of Change Healthcare, which provides a range of services to hospitals and clinics including processing pharmacy prescriptions and healthcare payments;

— on the heels of that incident, the BlackCat/AlphV operators reportedly plucked that payment back from the affiliate’s digital wallet before shutting down operations.

Got it?

Bleeping Computer says it’s unclear whether the closure is an exit scam or an attempt to rebrand the gang under a different name. BlackCat, the news service points out, is a rebrand of the DarkSide ransomware operation.

All this comes after American cyber authorities in December seized several of the group’s data leak and communications sites and published a decrypter that victim organizations can use to get access back to scrambled data.

It isn’t unknown why BlackCat/AlphV operators struck at one of its partners. Because of the December hit, the gang said it removed all of its rules forbidding affiliates allowed to use its ransomware to attack critical infrastructure like the healthcare sector.

In fact, the attack on Change Healthcare appeared to be a sign that BlackCat/AlphV had bounced back from the December blow.

Rick Pollack, CEO of the American Hospitals Association, called it “the most serious incident of its kind levelled against an U.S. healthcare organization.” According to Change Healthcare, he noted, the company processes 15 billion healthcare transactions annually and touches one in every three American patient records.

The incident is serious enough that, according to Politico, the White House’s National Security Council started looking into ways to provide short-term financial relief to U.S. hospitals. Arguably, attention from the White House is not what a ransomware gang wants.

The post Is the BlackCat/AlphV ransomware gang self-destructing? first appeared on IT World Canada.

Cyber Security Today, March 4, 2024 – A hacker is trying to trick the U.S. telecom regulator, WhatsApp gets to see Pegasus code and more

A hacker is trying to trick the U.S. telecom regulator, WhatsApp gets to see Pegasus code and more.

Welcome to Cyber Security Today. It’s Monday, March 4th, 2024. I’m Howard Solomon, contributing reporter on cybersecurity for ITWorldCanada.com and TechNewsday.com in the U.S.


Threat actors have been impersonating IT support staff to sucker people for years. According to researchers at Lookout, the latest version of this scam is aimed at employees of the U.S. Federal Communications Commission and at the cryptocurrency exchanges Binance and Coinbase. The goal is to trick staff into giving up their login credentials. It works like this: An employee would get a phone call or text supposedly from the company IT support staff saying their email account had been hacked. The employee would then be sent a text to their smartphone with a link that’s supposed to help them regain access to their account. What the employees would see is a fake login page created by a newly-discovered phishing kit that impersonates the single-sign-on services of Gmail, iCloud, Okta, Outlook, Twitter, Yahoo and AOL.

Employees need to be reminded of the dangers of taking for granted phone calls, texts or emails claiming to be from IT support — especially if they get links to supposed company login pages sent to their smartphones. Smartphones don’t always show the full address of a link, which makes it harder for users to spot something suspicious. Staff need to be reminded that just because part of a link includes a company’s name doesn’t mean its legit.

A Washington State radiology clinic is notifying over 235,000 people of a data theft. Yakima Valley Radiology says it learned in August of a theft of data from its systems including names and social security numbers.

Two American insurance companies are warning over 28,000 people of a theft of data from its third-party information processor. Fidelity Life Insurance and Empire Fidelity Investments Life Insurance are sending letters to people about the incident. The data was stolen last fall from Infosys McCamish Systems, which processes services for deferred compensation plans. Last month Infosys McCamish notified over 57,000 people of the data breach, including people with the Bank of America.

An Asian telecom manufacturer that routes millions of SMS text messages a day — including multifactor authentication codes — left a database with that sensitive information open for anyone who knew how to find it. According to TechCrunch, a security researcher found the database and needed the news service’s help to find the company that owned it. Public access to the database belonging to YX International has now been blocked.

WhatsApp and its parent Meta may get a look into the innards of the Pegasus commercial spyware, which has been sold to and abused by some government and law enforcement agencies around the world. WhatsApp is suing Pegasus developer NSO Group, alleging the spyware was used against 1,400 WhatsApp users for two weeks in 2019. A judge has ordered the company to hand over versions of Pegasus that would have been running in and around 2019. Commercial spyware works by exploiting vulnerabilities that application developers don’t know about.

To meet the shortage of IT workers with cybersecurity expertise colleges and universities are increasingly offering courses for students. But what should be in a course? The U.S. Cybersecurity and Infrastructure Security Agency has advice. It’s contained in a new publication called a Resource Guide for Cybersecurity Clinics. It has links to agency resources like its guidance for small businesses, how to create cybersecurity performance goals, how to create incident plans and more. The guide could also be useful to companies that want to create a cybersecurity training course — and IT leaders who don’t know how to create a cybersecurity strategy.

Finally, if you’re looking for a wireless doorbell camera to improve home security, buy one that can’t be hacked. Consumer Reports says many retailers like Walmart and Sears, and online marketplaces like Amazon, Shein and Temu, may be selling camera doorbells that could allow someone to know when you’re not home, or let them harass or threaten you. They can do it by capturing the WiFi video stream. The publication warns about devices with brand names of Eken, Fishbot, Rakeblue and Tuck. Any so-called smart devices that connects to your home internet network with a smartphone app — especially if it has a camera or a microphone — must have protection against being hacked. Do your research before buying.

Follow Cyber Security Today on Apple Podcasts, Google Podcasts or add us to your Flash Briefing on your smart speaker.

The post Cyber Security Today, March 4, 2024 – A hacker is trying to trick the U.S. telecom regulator, WhatsApp gets to see Pegasus code and more first appeared on IT World Canada.

Hashtag Trending Mar.4- Canadian police need a search warrant to access IP address; Musk sues OpenAI; World Server Throwing Competition too violent?

In Canada, your IP address has the right to remain silent. Elon Musk is suing OpenAI for not being Open. Apple faces a class action not allowing competitive access to backup services and the World Server Throwing Competition in March 2024 is accused of being too violent towards servers.  


All this and more on the “no servers were harmed in the making of this podcast ” edition of Hashtag Trending. I’m your host, Jim Love, CIO of IT World Canada and TechNewsDay in the US.

The Supreme Court of Canada has ruled that Canadian police must obtain a search warrant to access an individual’s IP address. This decision, passed with a 5-4 majority, underscores that an IP address, which serves as a critical link between an internet user and their online activity, carries a reasonable expectation of privacy under section 8 of the Charter, which protects against unreasonable search and seizure.

The ruling came from a 2017 case where Calgary police, investigating fraudulent online purchases, demanded a credit card processor to hand over IP addresses associated with certain transactions. This led to the arrest and conviction of an individual for 14 offenses after further obtaining subscriber information and search warrants. However, the Supreme Court has now clarified that obtaining IP addresses without judicial authorization constitutes an unlawful search.

This decision builds on a 2014 Supreme Court ruling that internet providers cannot turn over subscriber information to police without a search warrant. The court’s majority emphasized that the private nature of the information potentially revealed by an IP address warrants protection over governmental law enforcement interests. They highlighted how the internet has transformed privacy dynamics, concentrating vast amounts of personal data with third parties and enhancing the state’s informational capacity.

The ruling has sparked concerns among law enforcement, particularly in internet child exploitation units, about the potential for slowing down investigations. RCMP Sgt. Kerry Shima expressed worries that the decision could hinder the ability to act swiftly in cases, potentially putting children at risk and offering offenders greater opportunities to evade detection.

Our U.S. listeners may need a special note that in Canada, there is no distinction made in the press about which government regime appointed which judge so all we really know is that it was a 5-4 decision. 

Sources include: ITWorld Canada

Elon Musk has filed a lawsuit against OpenAI, a company he co-founded, and its CEO Sam Altman. Musk accuses OpenAI of shifting its focus towards profit rather than humanity’s benefit.  

Musk’s contention centers around OpenAI’s partnership with Microsoft, which he claims contradicts the organization’s original mission by making it a “closed-source de facto subsidiary” of Microsoft. 

Microsoft, under CEO Satya Nadella, has significantly invested in OpenAI and exclusively licenses the technology behind GPT-4, OpenAI’s advanced AI model. 

The lawsuit is posted on a number of sites, we’ll put a link in the notes. But while it’s provocative, it’s more than a little confusing. Musk notes in his lawsuit that Microsoft’s investment does not entitle it to any “ownership” in Automated General Intelligence. Interestingly, the suit also reveals that the board of OpenAI has the sole right to declare when AGI has been achieved. 

Musk presumably is complaining because he thinks that OpenAI has already achieved AGI in some form and is not sharing it with the world. 

But if OpenAI was an open source company, everyone would have access including Microsoft.

The lawsuit has sparked reactions among Silicon Valley’s elite, with venture capitalist and OpenAI investor Vinod Khosla and others exchanging criticisms on social media platforms. 

But this isn’t the only feud that Musk has going. He’s supposedly planning to create a Gmail competitor in response to Google’s AI biases and a challenge to humanoid robot startup Figure, backed by Jeff Bezos and others, as Musk develops his own robot at Tesla.

To anyone who has followed the extensive political lawsuits in the U.S. recently, Musk’s legal battle could expose a wealth of information about Musk, OpenAI, and a lot more companies and people, potentially affecting reputations and the operations of AI companies.

And as tantalizing as it might be to get some dirt on Musk, Google’s Larry Page, Sam Altman, Satya Nadella, Mark Zuckerberg and others, it really underscores the fact that a handful of billionaires and their whims and feuds control what might be the greatest scientific breakthrough since the invention of the digital computer or if you even partially believe the idea that AI could possibly, in the wrong hands, lead to the extinction of humanity, you have to ask yourself if these guys are the “right hands” to hold the future of humanity.

Sources include: Axios and The Verge has the text of the suit

Apple is facing a newly proposed class action lawsuit that accuses the company of unfairly monopolizing the cloud storage market for its devices by restricting device backups and other storage needs exclusively to its iCloud service. The lawsuit, reported first by Bloomberg Law, alleges that Apple has “marked up its iCloud prices to the point where the service is generating almost pure profit,” by rigging the competitive playing field.

The core of the complaint (pun not intended) is that Apple provides only 5GB of free iCloud storage, a limit that has remained unchanged since its introduction by Steve Jobs announced it in 2011. The plaintiffs argue that this amount of storage is insufficient for most users’ needs, compelling them to purchase additional iCloud storage plans.

The lawsuit focuses on the fact that iPhone users have no alternative but to use iCloud for full device backups. While users can choose other cloud-based storage providers, the lawsuit claims that Apple’s restrictions prevent rival platforms from offering a comprehensive cloud solution that can effectively compete with iCloud.

By making iCloud the only option for backing up Restricted Files and limiting the free storage to 5GB, Apple effectively forces device owners to use iCloud and pay for additional storage, the lawsuit alleges. It argues that there is no technological or security justification for this requirement, suggesting that Apple imposes it solely to limit competition and favour its iCloud service.

The lead plaintiff in the case is represented by Hagens Berman law firm, known for handling various class action lawsuits against Apple, including the notable $560 million Apple Books price-fixing lawsuit.

Individuals who have purchased iCloud storage and are interested in potentially joining the lawsuit are encouraged to do so via a form on the Hagens Berman website. 

Sources include: 9to5 Mac

The 2024 World Server Throwing Championship is set to take place at the annual CloudFest conference on March 19th. 

This unique competition, which began in Holland about a decade ago, has been described as an “intense underground sport” criticized for being “needlessly brutal to servers.” 

Emerging from its data-center basement origins, the WSTC as it is called is now stepping onto the world stage, inviting athletes to showcase their strength and skill in server throwing.

The event will be held outdoors in front of a live audience, welcoming up to 40 server-throwing athletes from all genders and ability levels. Participants will be given two attempts to throw a server as far as possible, with the top three performers winning prizes. While the sport’s nature is inherently brutal, safety measures such as wearing gloves are recommended due to some servers having very sharp edges.

The Dutch have established a strong presence in the sport, with the winner of a national championship event in 2022 managing to throw a server weighing over 10kg (22 pounds) a distance of 12.23 meters (over 40 feet).

CloudFest 2024 will be held in Rust, Germany. (I do not make this stuff up)

The event is described as essential for anyone working in the cloud industry, featuring keynotes, panel discussions, masterclasses, networking events, and more. Only paying attendees will have the opportunity to participate in the server-throwing competition, with tickets starting at 499 euros.

A shout out to Tom’s Hardware that did the groundbreaking journalism on this story.

Sources include: Tom’s Hardware

And that’s our show for today. 

Hashtag Trending goes to air five days a week with daily newscast and a weekend interview show that we creatively called – the weekend edition. 

xxx

Love your comments. 

Send us a note at jlove@itwc.ca or drop us a comment under the show notes at itworldcanada.com/podcasts – look for Hashtag Trending. 

Thanks for listening and have a Magnificent Monday.


The post Hashtag Trending Mar.4- Canadian police need a search warrant to access IP address; Musk sues OpenAI; World Server Throwing Competition too violent? first appeared on IT World Canada.

Fab wars: Intel, Tata Group, CG Power all launch foundry plans

With competition heating up in the foundry business – India this week approved three new semiconductor plants involving Tata Group and CG Power,, and is looking to achieve dominance in the industry – existing foundries have to up their game. Chief among them is Intel, which has been trying to recover from historical missteps that put it behind competitors such as TSMC and Samsung.

At its Intel Foundry Direct Connect event last week, it unveiled Intel Foundry, which will build not only its own chips, but products for anyone looking for fab services. It also announced a new organizational model.

“We’re not fixing one company, we’re establishing two vibrant new organizations,” said Intel chief executive officer Pat Gelsinger during his keynote. “Intel Foundry, to serve internal and external customers at scale, to manage supply chains, to assure capacity corridors, and Intel Products, our client, data centre and networking products. Two distinct and separate organizations.

“That begins today.”

AI, he said, will be incorporated everywhere, from data centre to cloud to network to edge to client, and it’s generating new excitement.

He noted, “When I showed up, it was like ‘This is boring. Here, let’s add a few more cores on the chip. Let’s make PCIe a little bit faster. Let’s increment the DDR. Boring.’ And then AI happened. End of boring. This is transforming everything about computing.”

And Intel plans to take advantage of this explosion of technology.

“Through our foundry, I want to manufacture every AI chip in the industry,” Gelsinger said. “Those internal that are being done by the cloud service providers, those merchant providers, the technology providers. We’re engaging in 100 per cent of the AI TAM [total addressable market]. And with that, we need a new model of what the foundry requirements are for that industry. And that’s, simply put, what we call the systems foundry for the AI era.”

Intel CEO Pat Gelsinger: “This is what we call a family photo mode. So, kids, come to papa, here we go – five nodes in four years.” Credit: Intel Corporation

He said that the company’s goal is to become the world’s number two foundry by 2030, and it will be the “world’s most sustainable foundry, committing to net-zero Scope 1 and Scope 2 GHG emissions by 2040, and net-zero upstream Scope 3 emissions by 2050.” It will also, he asserted, be the most resilient.

In 1990, 80 per cent of the semiconductors were built in US and Europe, Gelsinger noted. Today, 80 per cent are manufactured in a small concentrated area in Asia.

“We’ve seen this long, steady decline in terms of our supply chains for the world,” he said. “Nothing should be reliant on a single port to a single country, a single place in the world. We need resilience – resilient access to supply chains and capacity in the right regions at the right time. And thus the opportunity to drive systemic change, and where and how we drive the most important aspect of our future where the technology supply chains are. And as I’ve liked to say, the moonshot is 80/20 to 50/50 in a decade, rebalancing the supply chains of the world.”

Roadmap

Gelsinger also highlighted the company’s progress on its foundry process roadmap, announcing 14A, which he said is “venturing deeply into the Angstrom era,” as well as revealing extensions to existing nodes. And, he and Microsoft CEO Satya Nadella jointly announced that Microsoft has chosen Intel Foundry to build its own chip, based on the Intel 18A process.

Stuart Pann, senior vice president and general manager of Intel Foundry services, then took the stage to elaborate on the foundry’s activities.

“In this systems era, you can not only have to have open standards between devices, you have to have standards on the device.,” he pointed out, describing Intel as “a systems company turning into a foundry, not the other way around.”

But, he stressed, Intel can’t do it alone. Partners are key, and Intel has more than 30 ecosystem partners, including, he announced, Arm.

“This morning, we’re announcing a new partnership with Arm, an emerging business initiative. How do we take advantage of all the programs that Arm has to offer to bring design capability, design education out to all their customers. We’re doing this with Arm; we will make co-investments, will do joint programs, will provide shuttles at scale, Arm will provide IP at scale. And this is how we’re going to fuel this next wave of innovation.”

While Canada may not be in line for a fab (a semiconductor fabrication plant), at least not at the moment, Denis Gaudreault, Intel Canada country manager, said in an interview that this country is contributing in other ways.

Intel is now working with Markham-based ventureLAB, whose Hardware Catalyst Initiative supports the development of semiconductors, and has an R&D lab of its own on site. In fact, almost 90 per cent of Intel Canada’s employees in all locations work in engineering or development. And, he said, he’s continually looking for more ways that Canada can contribute.

The post Fab wars: Intel, Tata Group, CG Power all launch foundry plans first appeared on IT World Canada.

Canadian police need a search warrant to get your IP address: Supreme Court

How private is your internet address? Very, says the Supreme Court of Canada.

Police can’t just walk into a company and demand a suspect’s IP address by saying a Canadian resident doesn’t have an expectation of privacy of that information, the court ruled today. An IP address is vital enough that every resident expects it to be private, and it can’t be handed to police without a court order, the nation’s top court concluded.

“If s. 8 of the Charter [which says everyone has the right to be secure against unreasonable search and seizure] is to meaningfully protect the online privacy of Canadians in today’s overwhelmingly digital world, it must protect their IP addresses,” the court ruled in a 5-4 decision. “An IP address is the crucial link between an internet user and their online activity. Viewed normatively, it is the key to unlocking a user’s internet activity and, ultimately, their identity. Thus, an IP address attracts a reasonable expectation of privacy.”

Here’s the background: In 2017, Calgary police investigating fraudulent online purchases at a liquor store demanded a credit card processor hand over IP addresses for certain transactions. With the two IP addresses, police then got a production order from a judge compelling Telus to disclose the name and address of its customers at each IP address. Using this subscriber information, police got search warrants which led to a person being arrested and ultimately convicted of 14 offences.

The accused was convicted at trial, a decision upheld by the Alberta Court of Appeal. Both courts rejected his argument that his rights had been violated.

The case went to the Supreme Court to answer a question: Was obtaining the IP addresses a lawful search? No, said the majority.

Requiring that police obtain prior judicial authorization before obtaining an IP address “is not an onerous investigative step,” the court ruled. “Where the IP address, or the subscriber information, is sufficiently linked to the commission of a crime, judicial authorization is readily available.”

The court ordered the accused to face a new trial.

This isn’t the first time the Supreme Court has dealt with companies handing over internet-related data. In a 2014 decision, it unanimously ruled that Canadian internet providers can’t turn over basic subscriber information to police without a search warrant.

The minority in this case argued an IP address alone doesn’t have private information. “Without more, all an IP address reveals to the police is a user’s ISP [internet service provider] — hardly a particularly private matter, let alone core biographical information,” the minority judges wrote. The accused had little control over his IP addresses, which an ISP can change at will and without notice, the judges said. And, they noted, the search wasn’t carried out at the accused’s home, but at the credit card company.

That wasn’t persuasive to the majority. “In the informational privacy context, the claimant’s control over the subject matter [the IP address] is not determinative,” they wrote. “The internet requires that users reveal subscriber information to their ISP to participate in this new public square, and Canadians are not required to become digital recluses in order to maintain some semblance of privacy in their lives.”

“Defining a reasonable expectation of privacy is an exercise in balance,” said the majority. “In this case, the balance weighs in favour of extending a reasonable expectation of privacy to IP addresses.

“The intensely private nature of the information an IP address may betray strongly suggests that the public’s interest in being left alone should prevail over the government’s interest in advancing its law enforcement goals. The internet has exponentially increased both the quality and quantity of information stored about internet users, spanning the most public and the most private human behaviour. The internet has not only allowed private corporations to track their users, but also to build profiles of their users filled with information the users never knew they were revealing.

“By concentrating this mass of information with private third parties and granting them the tools to aggregate and dissect that data, the internet has essentially altered the topography of privacy under the Charter. It has added a third party to the constitutional ecosystem, making the horizontal relationship between the individual and the state tripartite. Though third parties are not themselves subject to s. 8, they mediate a relationship which is directly governed by the Charter — that between defendant and police. This shift has enhanced the state’s informational capacity.”

RCMP Sgt. Kerry Shima, acting officer in charge of Alert ICE, the internet child exploitation unit for Alberta, told CBC News that the ruling will slow down the unit’s investigations.

“This definitely throws a wrench into the machine. It’s going to put a lot of children at risk,” he said.

Shima said the ruling means police will not be able to act swiftly to tackle most of their cases in an “efficient manner.”

“It gives a wide berth for offenders on the internet and it gives an opportunity for people to hide even better and avoid detection,” Shima said.

The post Canadian police need a search warrant to get your IP address: Supreme Court first appeared on IT World Canada.

Healthcare sector “stretched thin” in fight against cyber attacks warns CSO of Health-ISAC

Healthcare organizations need more support from boards and governments to defend against the rising number of cyber attacks, particularly ransomware, says the chief security officer of a U.S.-based information sharing and analysis centre for the sector.

“Organizations are stretched thin, they just don’t have the people, budget to support the basic types of [cybersecurity] programs,” Errol Weiss, CSO of the Health-ISAC said in a recent interview.

“We need more resources for cybersecurity, everything including budget and appropriately trained and experienced staff to set up cybersecurity systems and to make sure they are being monitored and anomalies are being addressed quickly and mitigating controls are being put in place rapidily to close those holes.”

Two recent reports show what the sector is facing. Health-ISAC’s Q4 report for last year highlighted that ransomware attacks against the healthcare sector rose steadily throughout 2023.

Globally, 459 of 5,559 ransomware attacks hit the healthcare sector last year. The vast majority of them (379) were in the Americas (315 in the U.S. and 17 in Canada).

While initial compromises were often through poorly secured implementations of Windows RDP (remote desktop protocol) and compromised credentials, towards the end of the year many networks were penetrated by exploiting a vulnerability in devices running Cisco Systems’ IOS XE operating system (CVE-2023-20198).

The latest examples of the crisis: In the past seven days, the BlackCat/AlphV ransomware gang took credit for an attack on Change Healthcare, which processes pharmaceutical scripts for many hospitals, and the Rhysida gang said it was behind the attack on Chicago’s Lurie Children’s Hospital.

Health-ISAC also participated with the American Hospital Association in a just-released report for CISOs on the current and emerging healthcare cyber threats.

The number of healthcare-related data thefts globally averaged more than 86,000 records a day for the past 13 years, it found. “What’s even more troubling,” the report adds, “is that the number of incidents reported is increasing at an alarming rate.”

Although headquartered in Orlando, Fla., the Health-ISAC has 835 members in 100 countries, including 10 in Canada. Members include hospitals, clinics, insurance companies, pharmaceutical companies, medical device manufacturers, and electronic health software providers.

Health-ISAC charges membership fees based on revenue. For example, organizations that have under US$100 million revenue pay US$2,400 a year for access to threat intelligence.

Last year, it provided 39 targeted alerts to specific Health-ISAC member organizations to help teams mitigate potentially exploited vulnerabilities. It also delivered eight targeted alerts to member organizations where threat actors had already installed an implant using the Cisco IOS XE vulnerability.

Hospitals and clinics hold sensitive data of patients, which may put pressure on them to cave to ransom demands. And for-profit hospitals might seem to be logical targets in particular, because they would be seen as able to pay to get access back to encrypted and stolen data.

However, Weiss believes most ransomware attacks are opportunistic: Attackers exploit any opening at any organization they find. “I call it a shotgun method: They’re not aiming at anyone, they’re just casting a wide net.”

“They don’t even realize, when they obtain access to a victim’s network, what they have a foothold in,” he said.

However, once inside and when they realize what the victim organization is, gangs don’t hold back on their pressure tactics. “We have seen threats to release information including psychiatric care notes, even images of cancer patients, before and after pictures of surgeries — really horrific stuff,” Weiss said.

Asked why cybersecurity isn’t more of a priority in the sector, Weiss said that in the past several years, the rapid rise of ransomware is causing organizations to act. “We’re starting to see more discussion around what represents good minimum cyber hygiene, for example, when it comes to securing environments.”

Historically in the U.S., he said, healthcare institutions were focused on being compliant with privacy regulations. That has left “a large gaping security hole that an adversary could take advantage of.”

One recent aid: In January, the U.S. Department of Health and Human Services published Cybersecurity Performance Goals for the public health sector to follow.

The biggest mistakes organizations make are: not backing up data regularly, not patching vulnerabilities fast enough, and not implementing multifactor authentication to protect logins, Weiss said.

Asked why healthcare organizations aren’t doing those basics, he said it comes back to a lack of financial and human resources.

To move in the right direction, organizations sometimes have to decide between buying medical or IT equipment, he said. But they also have to realize that cybersecurity risks are “huge.”

“There’s going to have to be some hard decisions made when it comes to budgets,” he said. Government tax breaks for purchases and training IT staff will help, he added.

If things continue as they are, “we’ll continue to read about organizations becoming victims of the next cybercriminal organization,” he said. “The malware we’re getting is getting more sophisticated. Bad guys are constantly evolving their tactics to beat the system, and if organizations aren’t addressing that, there will be an impact.”

The post Healthcare sector “stretched thin” in fight against cyber attacks warns CSO of Health-ISAC first appeared on IT World Canada.

Cyber Security Today, March 1, 2024 – Warnings to GitHub users and Ivanti gateway administrators, and more

Warnings to GitHub users and Ivanti gateway administrators, and more.

Welcome to Cyber Security Today. It’s Friday, March 1st, 2024. I’m Howard Solomon, contributing reporter on cybersecurity for ITWorldCanada.com and TechNewsday.com in the U.S.


Developers who download code from the open-source GitHub repository always have to be careful they don’t get tricked by malicious packages. This is vital more than ever because since November a threat actor launched an automated campaign of uploading bad code into the repository. They hope this code will find its way into commercial or open-source applications, compromising millions of computers. According to researchers at Apiiro over 100,000 infected packages have recently been poured into GitHub. The threat actor behind this campaign clones existing packages, infects them and then re-loads them into GitHub. Then these bad packages are promoted to unsuspecting developers in forums. They collect login credentials of developers and anyone who uses an application the developer puts the bad code in. An estimated 99 per cent of bad packages have been removed by GitHub. But that still leaves thousands on the platform. And the campaign continues.

I’ve reported previously about the need for administrators of Ivanti Connect Secure and Policy Secure gateways to reset and patch those devices. Well, that isn’t enough. Cybersecurity agencies of the Five Eyes intelligence-sharing countries warned Thursday that threat actors can get around mitigations. In particular they can deceive Ivanti’s integrity Checker Tool to continue compromising these devices through three vulnerabilities. Administrators should consider dropping these devices, the agency say.

After years of company reminders and media reports about following safe cybersecurity practices some people still don’t get it. That’s a takeaway from a phishing report this week by Proofpoint. The company’s annual State-of-the-Phish report includes a survey of over 7,000 working adults in 15 countries. About a quarter admit they do risky things like use a work device for personal activities, reuse or share passwords and connect without using a VPN in a public place like a mall or airport. Some of these activities could be legitimate — there’s nothing wrong with sharing a password with a family member so they can access your personal email in an emergency. Or using an office computer to go to a website if its OK with management, like sites about your hobbies or to research a vacation. But the numbers suggest that some people do risky things because the security message isn’t getting through. A quarter of the respondents said they took risky action to meet an urgent deadline. Others did it to save time or money. Eleven per cent said they did it to meet a revenue target; 10 per cent did it to meet a performance objective. Here’s another factoid from the report: While 99 per cent of security pros surveyed said their organization has a security awareness program, only slightly more than half say they train everyone in the organization.

Speaking of phishing, Pepco Group, a European discount retailer, has acknowledged its division in Hungary recently lost the equivalent of US$16 million. How? Staff fell for a phishing lure.

Finally, a Malwarebytes researcher stumbled across a crook running an apartment reservation scam while trying to book a vacation in Amsterdam on Airbnb. The person who posted the apartment asked him to switch to communicating by email because Airbnb’s platform was allegedly having some problems. If interested, the owner said, they would send the traveler a link to Tripadvisor to complete the reservation. Well, the link went to a fake Tripadvisor website. The goal of this scam: To get an unsuspecting victim to click on a booking button on the fake Tripadvisor site and enter credit or debit card details. Two lessons: If someone asks you to switch communicating from one site to a different one or email when making any kind of purchase, be suspicious. And when you buy anything, do it on a full-screen computer or laptop, not a smartphone, so you can see the full email address of who you’re dealing with or the full website address of where you’re going.

That’s it for now. But later today the Week in Review podcast will be out. Guest Terry Cutler of Cyology Labs will join me to discuss how hard it is for law enforcement to put ransomware gangs out of business and Canada’s proposed law to make social media platforms take down child porn images fast.

Follow Cyber Security Today on Apple Podcasts, Google Podcasts or add us to your Flash Briefing on your smart speaker. Thanks for listening. I’m Howard Solomon

The post Cyber Security Today, March 1, 2024 – Warnings to GitHub users and Ivanti gateway administrators, and more first appeared on IT World Canada.

Hashtag Trending Mar.1- HP debacle; Humanoid robots closer to hitting our workplaces; Apple blew $10 billion on the electric car before pulling the plug

If rumours are true and this one should be, I started it, we have a special edition of the Weekend show where we talk about the evolution of the role of the CIO with two incredible CIOs as the CIO Association of Canada turns 20. Don’t miss it. 

MUSIC UP

Can HP make you love them again? Humanoid robots with AI might be closer than we think. Researchers find that talking like a character from Star Trek can improve your AI results. And how many iPhones would it take to make up the money Apple blew before it killed its self-driving electric car?


All this and more on the “you can’t make this stuff up” edition of Hashtag Trending. I’m your host, Jim Love, CIO of IT World Canada and TechNewsDay in the US.

HP is trying to make you love them again. 

We love the price of these printers, but who among you has not gone to buy ink for that new purchase then asked yourself if it wouldn’t just be cheaper to buy a new printer again?

We always knew that the ink jet printers were a lot like shaving razors. They’ll give you the printer to get you hooked, and then you have to buy the ink.

Which generated a whole industry of refilling cartridges and then third party or no-name ink. 

So printer manufacturers, HP being the most well-known, started making their printers so they wouldn’t allow cheaper third party ink. They said it was for our own good – because these knock off cartridges could harm our printer. 

That didn’t go over well. People felt they bought the printer, and then they had the right to do whatever they wanted.

So HP tried – ink on subscription. But people who didn’t use up their limit on printers were complaining that they shouldn’t have to pay for more ink than they used.

So HP is trying another tactic. 

Their All-In-One plan lets you rent the printer, starting at a low price of $6.99 US per month.

You get the printer. You get the ink. You get a guarantee that subscribers to the HP All-In Plan will receive a new printer and all the ink they need, along with access to HP’s “24/7 Pro Live support.” If a subscriber encounters a problem that HP cannot fix remotely, the company promises to replace the faulty printer the next business day for free.

They eliminate the “never-ending struggle” of printer ownership by providing a hassle-free printing solution.

Will this make you love HP again? Will this stop the criticism and class action suits?

It might – until you read the fine print. Yes, it’s $6.99 per month but you can only print 20 pages each month. After that, you pay more, depending on the number of pages. You can pay between $8.99 up to $60.99

I predict that the next Reddit post will be about someone who bought this All In One package and got a much bigger bill than they thought. 

Sources include:  [PCMag](https://www.pcmag.com/news/hp-targets-the-haters-with-printer-rental-subscription-plan).

How long do you think it’s going to be before humanoid robots hit the workforce.

And will they be able to fix the printer?

Hint: There’s some of them working now in companies ranging from BMW to even Canadian Tire.

And don’t be surprised if they can do some incredibly intricate things.

A new humanoid robot startup Figure has attracted significant attention and investment, with a “who’s who” of Silicon Valley ponying up enough to give the company a valuation of $2.6 billion. 

Figure is at the forefront of integrating bipedal robots with dexterous hands into the labour force, and there’s a lot of other companies trying to get in on the action.

So guess who is working with this robot manufacturer Figure? You don’t need an AI to figure out that OpenAI’s is working to bring capabilities in processing and reasoning from language to humanoid robots

But do not worry. We have assurances from robotics companies that these robots are not here to take our jobs. They will at first undertake tasks that are too dangerous or repetitive for humans. And they emphasize “upskilling” as a strategy to retrain displaced workers for more fulfilling roles within the same field.

Then they’ll replace us. 

But that’s a long way off. Right? Nope. Silicon Valley’s Brett Adcock, the “flying taxi” pioneer, thinks we’ll see robots move into the workforce in about 2 years. 

And I put some links to videos in the show notes. It’ll make you wonder.

As the late Jimmy Buffet said, “my occupational hazard is being…my occupation’s just not around.” 

Sources include: Axios

Robot  moving a crate to a conveyor belt

Robot making coffee

Tesla’s Robot Optimus taking a stroll 

Sanctuary’s Phoenix taking your blood pressure.

Forget all those prompt management course on YouTube. 

A new study has revealed that AI chatbots perform better at solving grade-school-level math problems when prompted to respond as if they are a Star Trek character. 

Two researchers from VMware in California conducted a study, which was initially reported by New Scientist and published on arXiv on February 9, 2024. 

Their investigation aimed to explore the impact of “positive thinking” prompts on AI performance, a concept that has gained attention among those working to optimize chatbot outputs. 

I’ve read stuff like this before where emotional prompts appear to work better. One study said that if you put emotion into your prompt, it would work. I started saying that I would be fired if the answers were wrong. 

I don’t know if it worked, but it’s like chicken soup. “Can’t hoit.”  

It just points out how little we really know about how these incredible algorithms can display behaviours that we don’t understand.

These researchers thought “positive thinking” should not influence a computer system’s performance, but they may have found evidence suggesting otherwise.

The study involved feeding three Large Language Models (LLM) — Mistral-7B5, Llama2-13B6, and Llama2-70B7 — with 60 human-written prompts designed to encourage the AIs. These prompts varied from motivational statements like “This will be fun!” to affirmations of the AI’s capabilities. The models were then tasked with solving the GSM8K, a dataset of grade-school-level math problems, to determine the effectiveness of each prompt.

So what were the best-performing prompts for the Llama2-70B model?  

Talk like Star Trek. 

Their prompt specifically requested the AI to navigate through turbulence and locate the source of an anomaly, using phrases reminiscent of a Starfleet commander’s log. This Star Trek-themed prompt significantly improved the model’s math-solving abilities, a result that both surprised and puzzled the researchers.

The study underscores the unpredictable nature of AI systems and the intricate factors that can influence their performance. While the exact reasons behind the Star Trek prompt’s effectiveness remain unclear, it suggests that the way questions are framed can dramatically impact AI output quality. 

Catherine Flick, a researcher at Staffordshire University, UK, commented on the findings, emphasizing that AI models do not truly understand the context of the prompts but rather access different sets of weights and probabilities based on the input.

This research shows how little we know about AI behaviour. So add that to your list of ways to optimize AI performance through carefully crafted inputs. 

Is this guy really telling me my prompts will be better if I talk like a Star Trek character. I know what you are thinking. 

Captain, I can’t believe my ears.  

I canno believe your ears either, Mr. Spock.

Sources include: Business Insider

And speaking of costing more than you thought possible….

We covered the story about the demise of Apple’s self driving electric vehicle called “Project Titan.”  

Apparently, Apple blew a cool $10 billion on that project before they pulled the plug. (I will never tire of that pun – tire – get it?) 

And it turns out that this might have been Dodgy from the beginning (Dodgy?) 

Some employees called the project “the Titanic disaster,” reflecting doubts about its feasibility. Okay, I can’t outdo that one. Titan – Titanic. They were asking for that.

It seems the only smart move Apple made was not buying Tesla.  They were in discussions with Elon Musk but Apple ultimately decided it would be too hard to integrate Tesla into its “ecosystem.”

Yeah. But they put the brakes on that deal (gotta love it) and missed the bonus of having Elon associated in some way with the Apple brand. 

But you know something? Apple still has hundreds of millions in cash and plans to leverage the knowledge and innovations gained from working on the car, including AI-powered AirPods with cameras, robot assistants, and augmented reality technologies.

So all of that IP will have a new lease on life. 

Couldn’t resist.

Sources include: Mac Rumors

And that’s our show for today. And what a strange day it was. 

Hashtag Trending goes to air five days a week with daily newscast and a weekend interview show that we creatively called – the weekend edition. 

Love your comments. 

Send us a note at jlove@itwc.ca or drop us a comment under the show notes at itworldcanada.com/podcasts – look for Hashtag Trending. 

Thanks for listening and have a Fantastic Friday.


The post Hashtag Trending Mar.1- HP debacle; Humanoid robots closer to hitting our workplaces; Apple blew $10 billion on the electric car before pulling the plug first appeared on IT World Canada.

MWC Barcelona 2024 news roundup: Telecom, AI, security and more

MWC Barcelona 2024 comes to a close today. Here’s a look at some of the announcements that the event brought to light, from industry leaders like Cisco, Google, Intel and others, spanning artificial intelligence, telecom, security and sustainability.

Telecom

Cisco has partnered with Telus to launch new 5G capabilities for IoT use cases across industry verticals, notably connected cars. Car original equipment manufacturers (OEMs) will be able to offer new on-board applications and advanced driver assistance system (ADAS) services while pursuing other revenue diversification goals, said Cisco.

Further, U.S.-based data infrastructure semiconductor solutions provider Marvell Technology, announced that it is collaborating with Dell, Fujitsu and Wind River to deliver Open RAN solutions for Japanese mobile phone operator NTT Docomo and other carriers.

ORAN is a nonproprietary version of the Radio Access Network (RAN) system that allows interoperation between various pieces of cellular network equipment provided by different vendors, including the radio unit (RU), the distributed unit (DU) and the centralized unit (CU).

A big focus for numerous other companies at MWC, ORAN expected to account for 20-30 per cent of worldwide RAN revenues by 2028, according to the Dell’Oro Group.

Singapore-based SynaXG, for instance, announced a strategic collaboration with Wind River and Ampere. The partnership integrates SynaXG’s virtualized distributed unit (vDU) card with StarlingX, a cloud-native, Kubernetes, open-source infrastructure project supported by Wind River and Ampere’s multicore processors to redefine 5G network infrastructure.

The collaboration sets new industry standards for power efficiency, ease of integration, and cloud-based network management for Open RAN, said SynaXG.

Germany-based ng-voice launched Hyperscale IMS, a cloud-native instant messaging system solution to empower telecom operators to reduce voice production costs, optimize network management and service delivery with AI and deploy new voice services for additional income streams.

AI

Telematics company Geotab, attending MWC as part of Ontario’s delegation, introduced Geotab Ace, a generative AI assistant for connected transportation.

The tool has access to an expansive array of insights, the company said, including predictive safety analytics, predictive maintenance, trip data, zone activity, electric vehicle statistics, exception events, GPS tracking, and more. It’s built on privacy-by-design principles, and never shares customer telematics data with any Large Language Model (LLM), said Geotab.

Further, Arizona-based telecom equipment supplier Viavi announced additional capabilities of a joint Testbed as a Service (TBaaS) with VMware (recently acquired by Broadcom) to advance digital twin environments.

The digital twin modeling, based on AI and enabling new predictive capabilities, will be leveraged for the evaluation and performance benchmarking of applications.

In other AI news, users now have access to Google’s generative AI assistant, Gemini, in Gmail, Docs, Slides, Sheets and Meet (formerly Duet AI), with a Google One AI Premium plan. The tech giant highlighted that no personal or business Workspace data will be used to train underlying LLMs, without permission.

The Google One AI Premium plan costs US$19.99 per user per month after a no-cost two month trial.

Finally, American messaging platform, Gupshup announced that it is integrating AI chatbots, powered by Google’s Vertex AI, to rich communication services (RCS) conversations. That, the company said, “will enable businesses to deliver more precise and human-like interactions with speed and scale and offer a more personalized and responsive experience.”

Security

Palo Alto Networks announced end-to-end private 5G security solutions and services, in partnership with Celona, Druid, Ataya, NETSCOUT, Nvidia and NTT DATA.

Specifically, Palo Alto Networks’ enterprise-grade 5G Security, along with the partner integrations, seek to enable organizations to easily deploy, manage, and secure networks throughout their entire 5G journey.

Furthermore, endpoint security solutions provider, BUFFERZONE introduced the NoCloud AI anti-phishing detection solution, which runs on Intel’s processors. The company said it uses multiple deep-learning engines that work together to uncover malicious behavior, enabled by the Intel technology.

NoCloud AI has been added to BUFFERZONE’s Safe Workspace platform and integrated as a Chrome or Edge browser extension.

Meanwhile, Viavi announced the addition of traffic analysis capabilities to Observer Sentry, its Software-as-a-Service-based threat exposure management solution. The new capabilities will allow Observer Sentry to go beyond identifying unintended and dangerous exposures, and help SecOps, DevOps and cloud architects determine whether a vulnerability has been exploited.

Sustainability

Orange Business signed a Memorandum of Understanding (MoU) with Cisco for a joint action plan to help reduce their greenhouse gas (GHG) emissions. Further, the collaboration will allow Orange Business to provide their customers with an estimate of the GHG emissions from their products and solutions based on Cisco technology.

Secondly, GSMA, unveiled a network equipment commerce platform, in partnership with Shields Environmental Group, to help the telecom industry achieve its financial and environmental sustainability goals.

The platform will be available to more than 1000 mobile operators and equipment manufacturers globally.

Finally, NTT Data and Schneider Electric announced a partnership combining NTT DATA’s Edge as a Service, which includes fully managed edge to cloud, private 5G, and IoT capabilities, with Schneider Electric’s EcoStruxure, a modular data center. The partnership seeks to enable companies to maximize energy efficiency while meeting the demands of compute-intensive tasks such as machine vision, predictive maintenance, and other AI inferencing applications at the edge.

Discover in detail all MWC Barcelona announcements here.

The post MWC Barcelona 2024 news roundup: Telecom, AI, security and more first appeared on IT World Canada.